Alex Stamos says AI has flipped the hacker kill chain, and security is entering a "dark age"
Cognition's security chief describes chained breaches from Fireworks to Cursor to 5,000 companies, and a downloadable Chinese tool that finds and exploits bugs in real time.
 DevIsDead Newsroom
If security teams sound exhausted lately, Alex Stamos says there's a reason. The chief security officer at Cognition and Stanford lecturer told Nilay Patel on The Verge's Decoder that AI has put the industry on something like permanent emergency footing, and that we're in for a rough stretch before things improve.
What's been happening
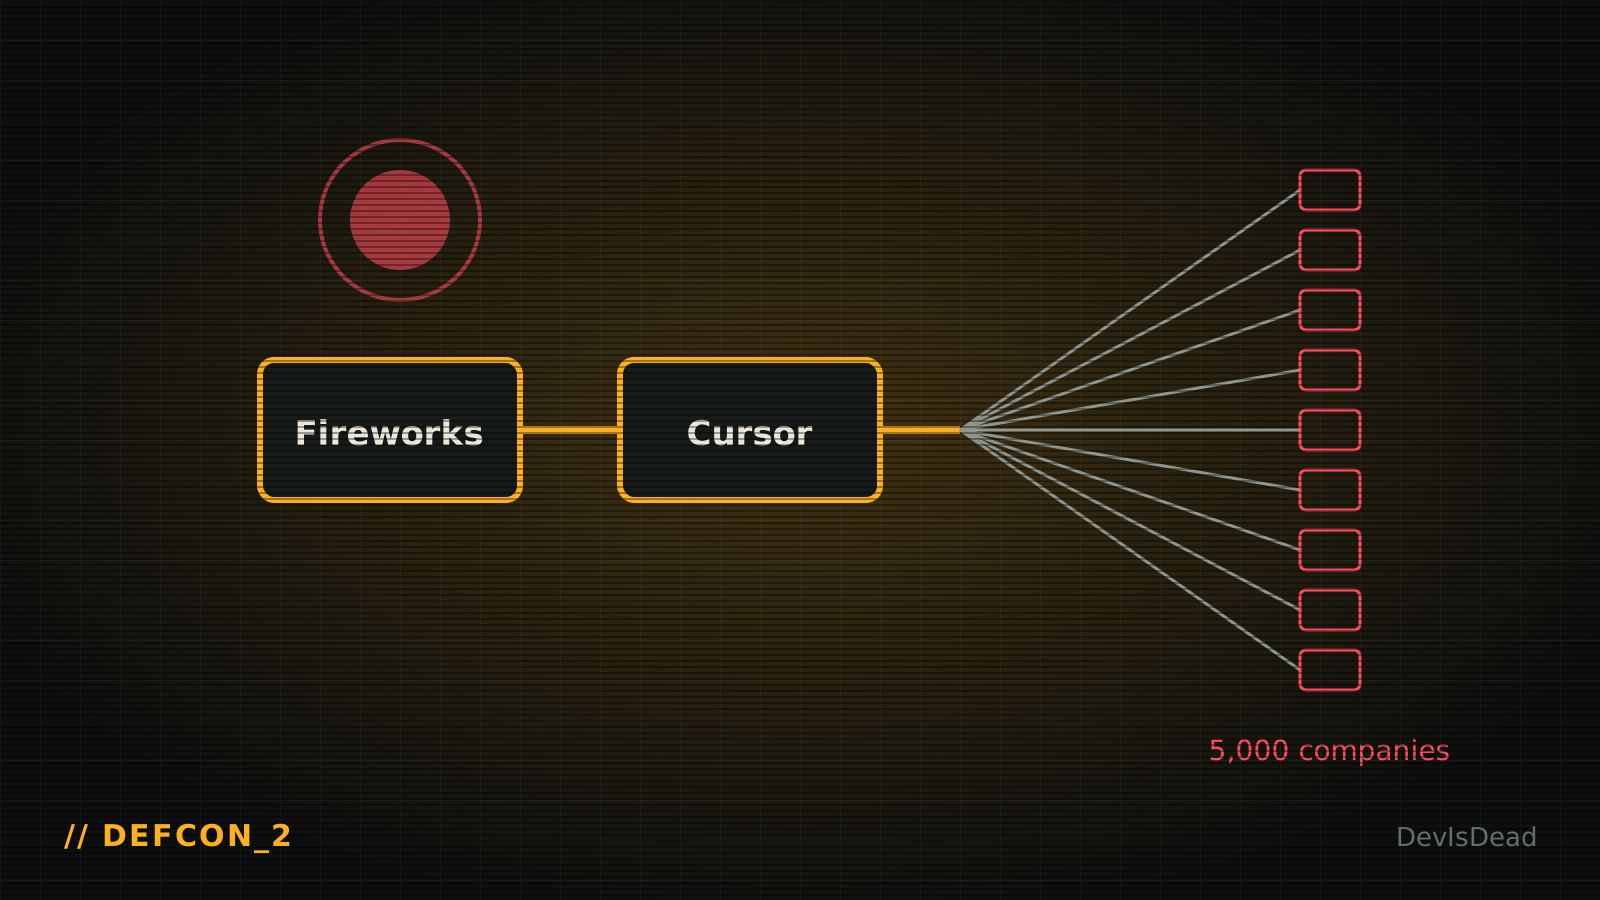
Stamos pointed to a run of incidents: big bugs in PHP and Node, a string of breached neoclouds, a Binance heist he called the largest in history, and chained attacks. In one chain, API keys stolen from AI provider Fireworks were used to break into Cursor; from there attackers pushed a malicious plugin that reached 5,000 more companies. He described it as a continuous breach across the tech industry, and said fellow security chiefs have been at "DEFCON 2" since October.
The inverted kill chain
His core point is how attacks now work. Traditionally, attackers researched software, found a bug and wrote exploits in advance, then deployed them. Now, he says, open-weight models are good enough to automate most of the kill chain: an AI system looks at a target, finds bugs and writes exploits on the spot.
The tool everyone is talking about, he says, is ARTEX, a Chinese open-source project with an English translation on GitHub. Paired with an "abliterated" GLM-5.3, a version with safety training removed, it lets people break into a shocking number of organizations. It hit three South Korean banks first, and about 200 more companies this week. Not since the 1990s, he says, could you download a free tool and break into billion-dollar companies.
Not doom, but dark
Stamos isn't a long-term doomer. He compares the moment to the early, chaotic days of the always-online internet and expects defenses to adapt. But he expects a "dark age" first.
This matches the Vals test results showing free models closing in on gated ones. For developers, the practical steps are familiar but urgent: rotate and scope API keys, treat plugins and extensions as supply chain risk, and assume your dependencies are being scanned by an AI right now.
Scoreboard update: AI +1. AI turns finding bugs and writing exploits into a single automated loop.
Stay undead.
Comments 0